 Data Exfiltration
Cross-Session Query Correlation as an Early Signal of Incremental Context Extraction
Linking queries across sessions may expose extraction attempts that per-session guardrails miss.
Bianca Espinoza·
 Prompt Injection
Behavioral Anomaly Detection When Third-Party Plugins Feed Adversarial Instructions to Enterprise LLMs
Runtime behavioral monitoring catches plugin-based prompt injections that content filters miss.
Bianca Espinoza·
 Prompt Injection
Plugin and Connector Trust Boundaries That Stop Adversarial Instruction Propagation
Architectural trust boundaries stop external content from hijacking AI agents and their tools.
Bianca Espinoza·
 LLM Security Fundamentals
A Repeatable Workflow for Mapping Third-Party LLM Vendor Risk to OWASP and NIST Without Manual Effort
Automate vendor LLM risk assessment by mapping it to OWASP and NIST frameworks continuously.
Bianca Espinoza·
 Data Exfiltration
Runtime Behavioral Baselines for Detecting Adversarial Query Campaigns Against Vendor LLM APIs
Behavioral baselines reveal attack patterns hidden in individual queries.
Bianca Espinoza·
 AI Agent Security
Confused Deputy Attacks in AI Agent Systems
AI agents mistake untrusted content for instructions when they hold authority the author lacks.
Bianca Espinoza·
 LLM Security Fundamentals
Automated Dual-Framework Scoring of Third-Party AI Vendors Against OWASP LLM Top 10 and NIST AI RMF
Automated scoring maps vendor AI risks to security frameworks for continuous governance.
Bianca Espinoza·
 AI Security Governance
EU AI Act Compliance Requirements for High-Risk AI Systems
Annex III systems must comply by December 2027, while Annex I systems get until August 2028.
Bianca Espinoza·
 AI Security Governance
AI Risk Governance Roles and Responsibilities in Large Enterprises
Enterprises fill governance forms while AI systems operate unsupervised—naming owners fixes the gap.
Bianca Espinoza·
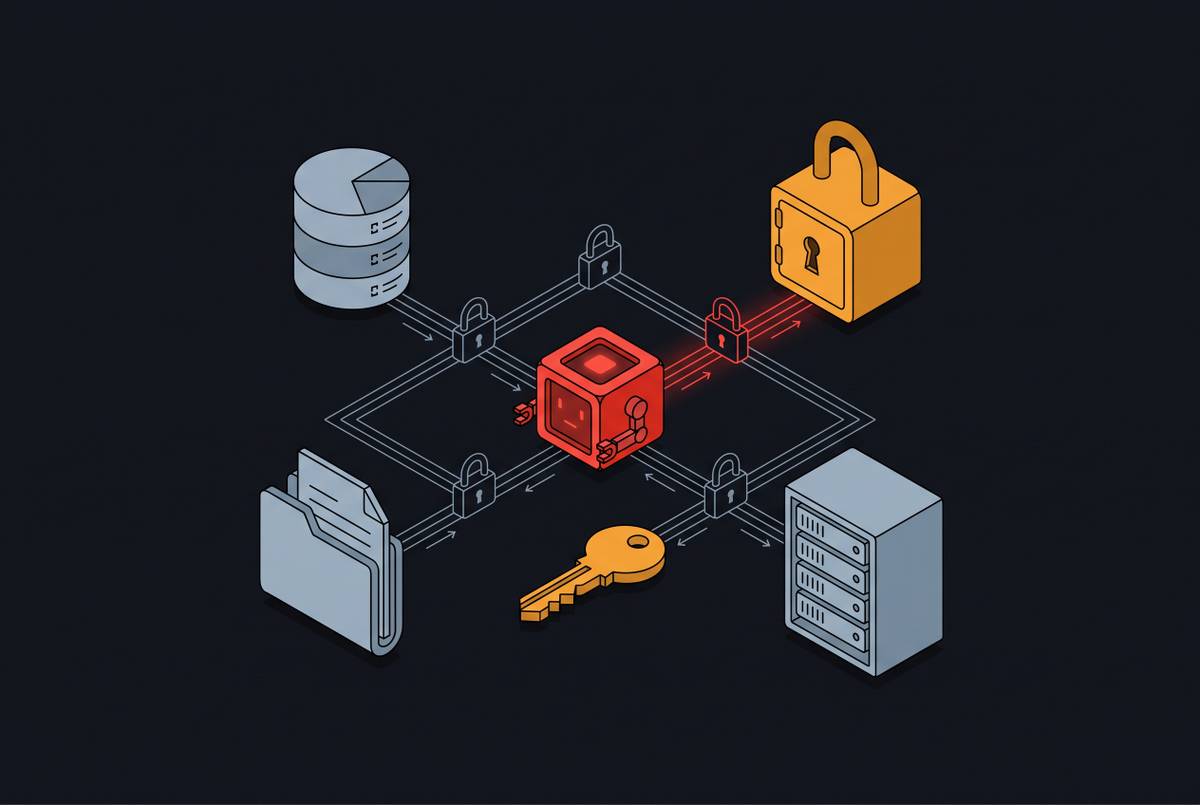 AI Agent Security
Least Privilege Principles Applied to AI Agents
Static roles can't contain agents that reason, and breaches show it.
Bianca Espinoza·
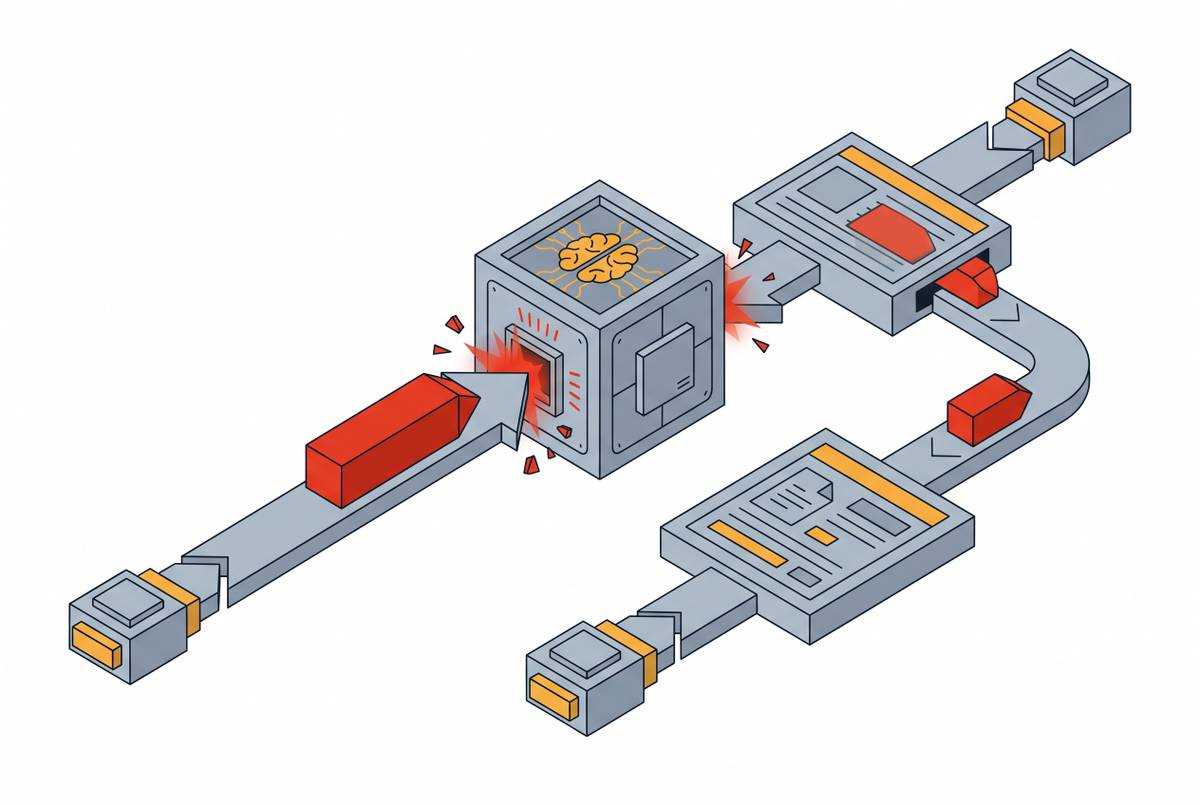 Prompt Injection
Direct vs Indirect Prompt Injection Explained
Direct attacks hit the chat box; indirect ones hide in content.
Bianca Espinoza·
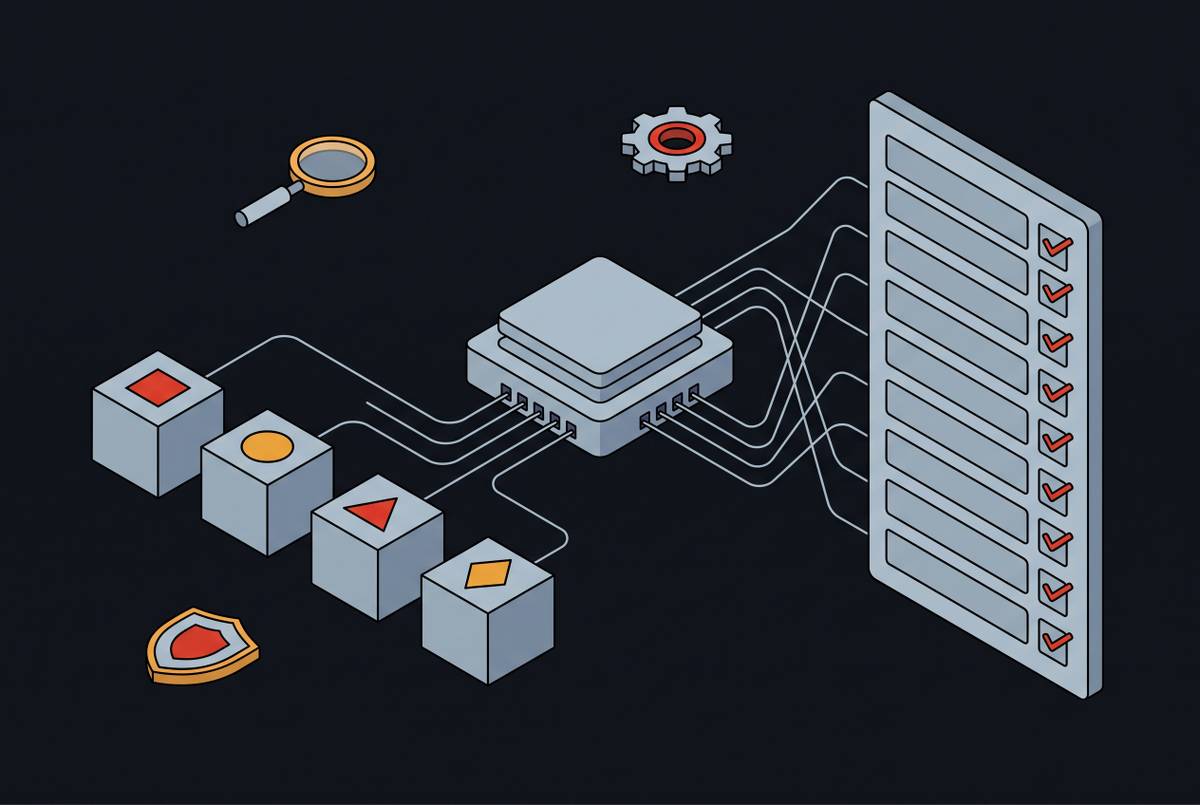 LLM Security Fundamentals
Tools That Map Third-Party AI Vendors to the OWASP LLM Top 10
Mapping vendor AI risks to OWASP standards reveals where enterprise exposure actually hides.
Bianca Espinoza·
 Prompt Injection
Guard LLM Approaches to Prompt Injection Detection
Fine-tuned classifiers catch most injections, but evasion techniques defeat them consistently.
Bianca Espinoza·
 AI Security Governance
NIST AI RMF Applied to LLM Deployments
Most organizations document NIST compliance but never run it against live LLM deployments.
Bianca Espinoza·
 Prompt Injection
 vs Jailbreak
Prompt injection and jailbreaking attack different system layers and require separate defenses.
Bianca Espinoza·
 AI Vendor Risk Analysis
AI Plugin and Connector Security Risks in Enterprise Platforms
Credentialed AI plugins create insider threats that existing security controls can't detect.
Bianca Espinoza·
 AI Vendor Risk Analysis
AI-native versus adapted third-party risk platforms for LLM threat coverage
Enterprises need visibility into third-party AI risks traditional vendor platforms can't detect.
Bianca Espinoza·
 Data Exfiltration
Covert Channel Data Exfiltration in LLM Agents
Attackers use hidden instructions to turn agent tools into data exfiltration channels.
Bianca Espinoza·
 Data Exfiltration
How LLMs Leak Training Data
Models memorize fragments word-for-word and hand them back to anyone who asks the right way.
Bianca Espinoza·
 Data Exfiltration
Preventing PII Exfiltration in Customer-Facing LLM Chatbots
Three attack pathways expose customer data in AI chatbots, each requiring separate defenses.
Bianca Espinoza·
 LLM Security Fundamentals
Overreliance on LLM Output as a Security Risk
The system, not the user, is where LLM security risk actually lives.
Bianca Espinoza·
 LLM Security Fundamentals
Training Data Poisoning Attack Vectors
One in four organizations has detected AI data poisoning; the actual number is likely far higher.
Bianca Espinoza·