Prompt Injection
Semantic Integrity Checks That Catch Injected Instructions Inside RAG Retrieved Chunks
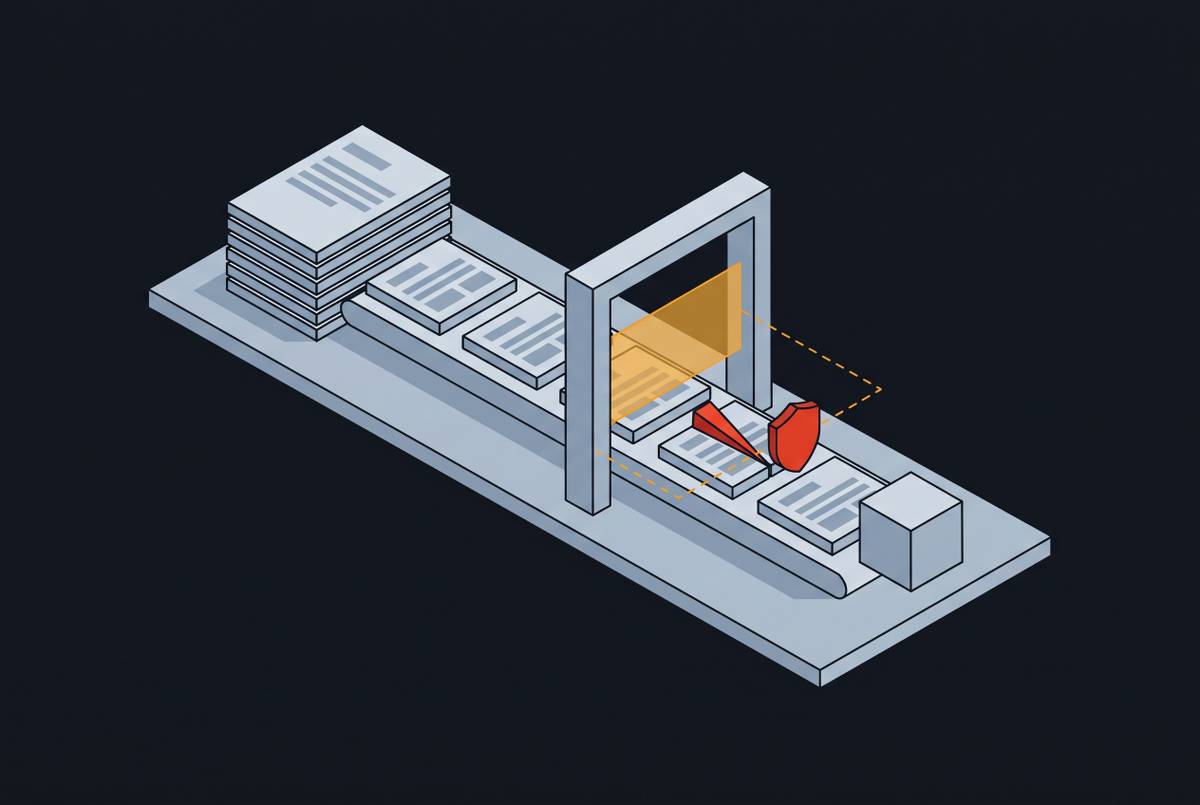
Multiple detection layers catch both explicit and semantic injection attacks in RAG systems.
Selah Beck
· 8 min read
Multiple detection layers catch both explicit and semantic injection attacks in RAG systems.
Vendors' detection placement and payload coverage determine whether RAG systems stay safe.
Protect AI systems by catching poisoned documents before they enter the knowledge base.
Automate vendor LLM risk assessment by mapping it to OWASP and NIST frameworks continuously.
Security teams now pair OWASP threat lists with NIST governance to audit AI vendors continuously.
Behavioral baselines reveal attack patterns hidden in individual queries.
Secure RAG systems by filtering malicious payloads at every pipeline stage.
OWASP and NIST findings feed one supplier risk program when mapped as evidence.
AI agents mistake untrusted content for instructions when they hold authority the author lacks.
Securing AI agents requires isolation between instructions and data before models gain tool access.