LLM Security Fundamentals
Automated Dual-Framework Scoring of Third-Party AI Vendors Against OWASP LLM Top 10 and NIST AI RMF
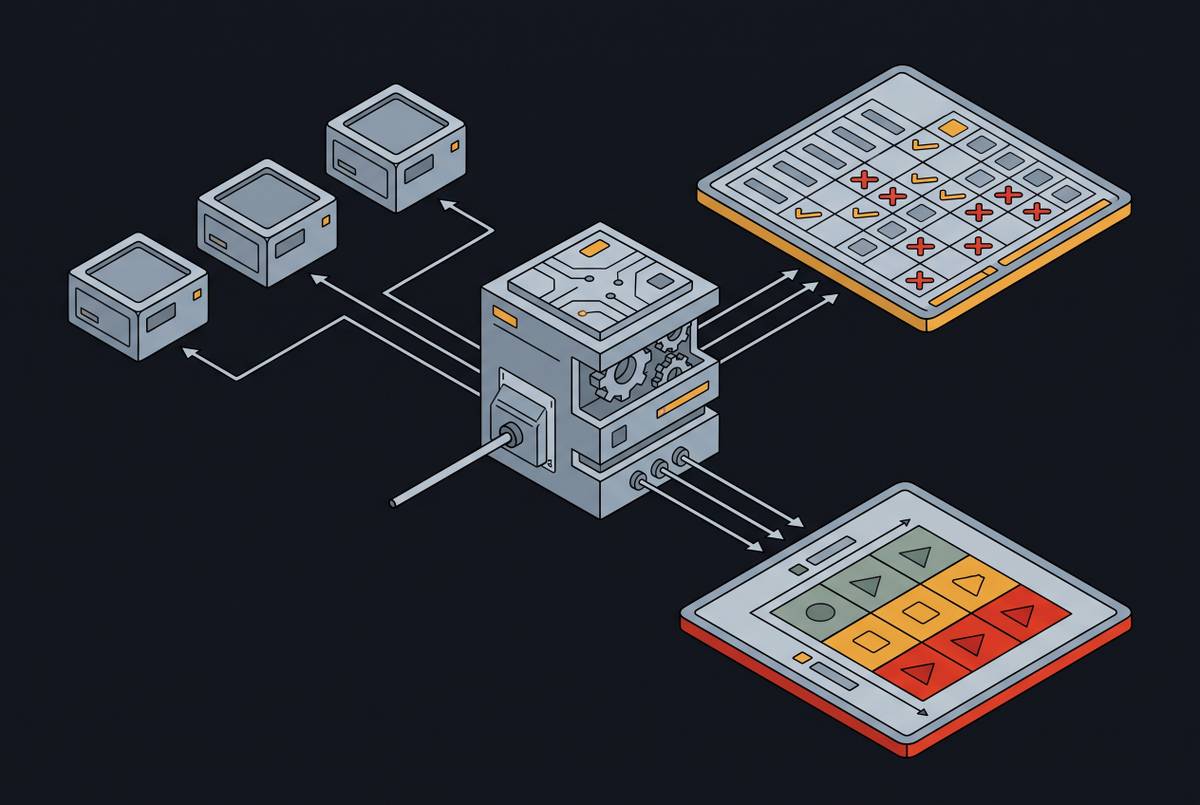
Automated scoring maps vendor AI risks to security frameworks for continuous governance.
Bianca Espinoza
· 10 min read
Automated scoring maps vendor AI risks to security frameworks for continuous governance.
The standard certifies governance systems, not model performance or fairness.
How deployment context, not model choice, determines EU AI compliance obligations.
Regulators now require detailed AI documentation that most companies still aren't providing.
Boards now face legal liability for weak AI oversight, not just reputational risk.
AI systems violate the three core assumptions traditional vendor risk assessment depends on.
Annex III systems must comply by December 2027, while Annex I systems get until August 2028.
Companies need named owners for each AI system, not just policies on paper.
Enterprises fill governance forms while AI systems operate unsupervised—naming owners fixes the gap.
Auditing frameworks lack controls designed for AI systems that operate autonomously across vendors.
Approval checkpoints alone won't stop rogue AI agents from causing real-world harm.
Attackers exploit how AI agents trust tool descriptions without checking if they change mid-session.