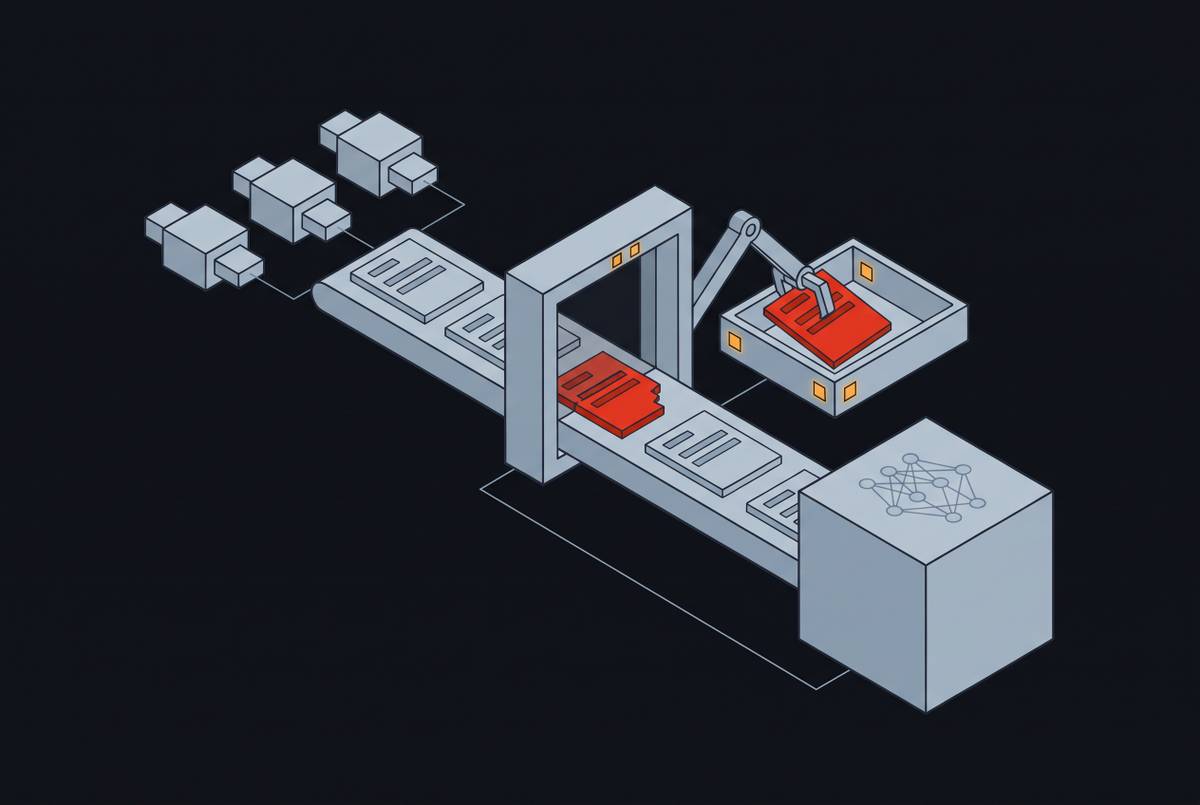
 Prompt Injection
Detecting Poisoned Documents in External Connector Pipelines Before They Manipulate AI Responses
Protect AI systems by catching poisoned documents before they enter the knowledge base.
Marco Quist·
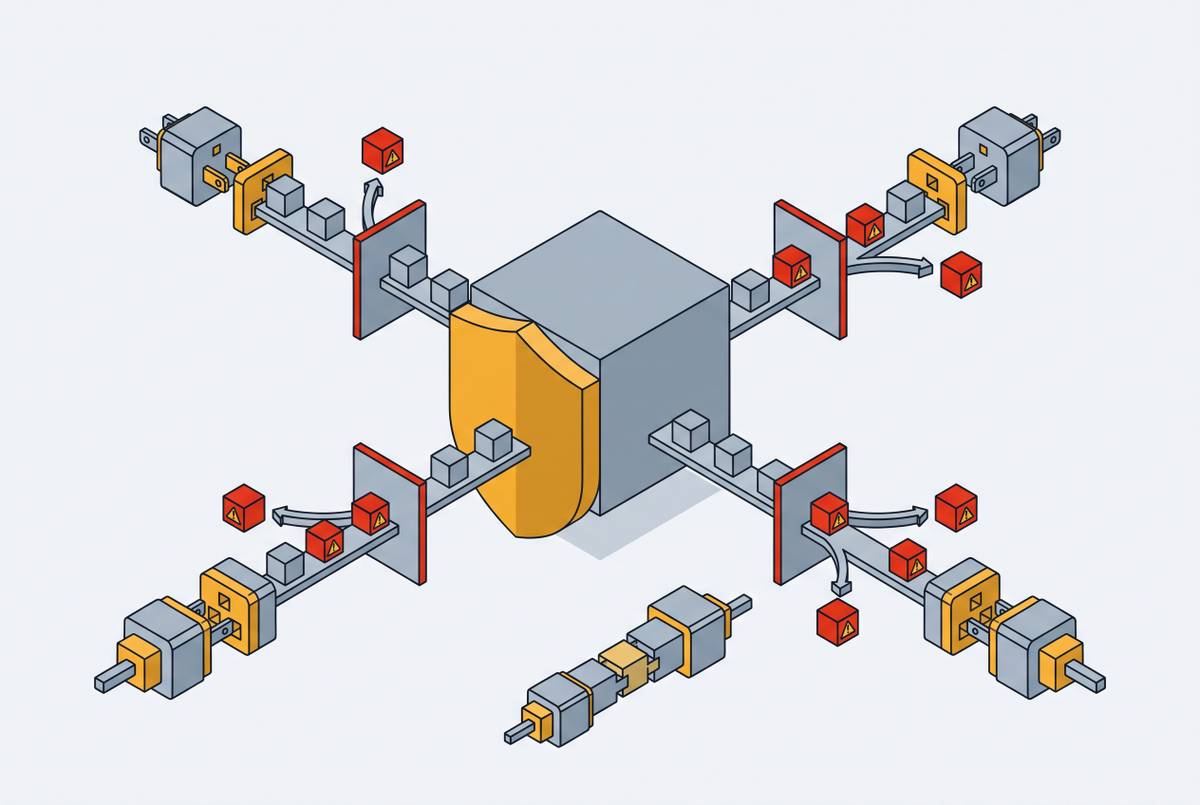 Prompt Injection
Hardening the RAG Retrieval Layer Against Injected Payloads in Third-Party Connectors and Plugins
Secure RAG systems by filtering malicious payloads at every pipeline stage.
Marco Quist·
 AI Security Governance
EU AI Act Obligations for High-Risk LLM Applications
How deployment context, not model choice, determines EU AI compliance obligations.
Marco Quist·
 AI Security Governance
Board-Level AI Risk Reporting Metrics and Frameworks
Boards now face legal liability for weak AI oversight, not just reputational risk.
Marco Quist·
 AI Security Governance
AI Governance Gaps in SOC 2 and ISO 27001 Audits
Auditing frameworks lack controls designed for AI systems that operate autonomously across vendors.
Marco Quist·
 Prompt Injection
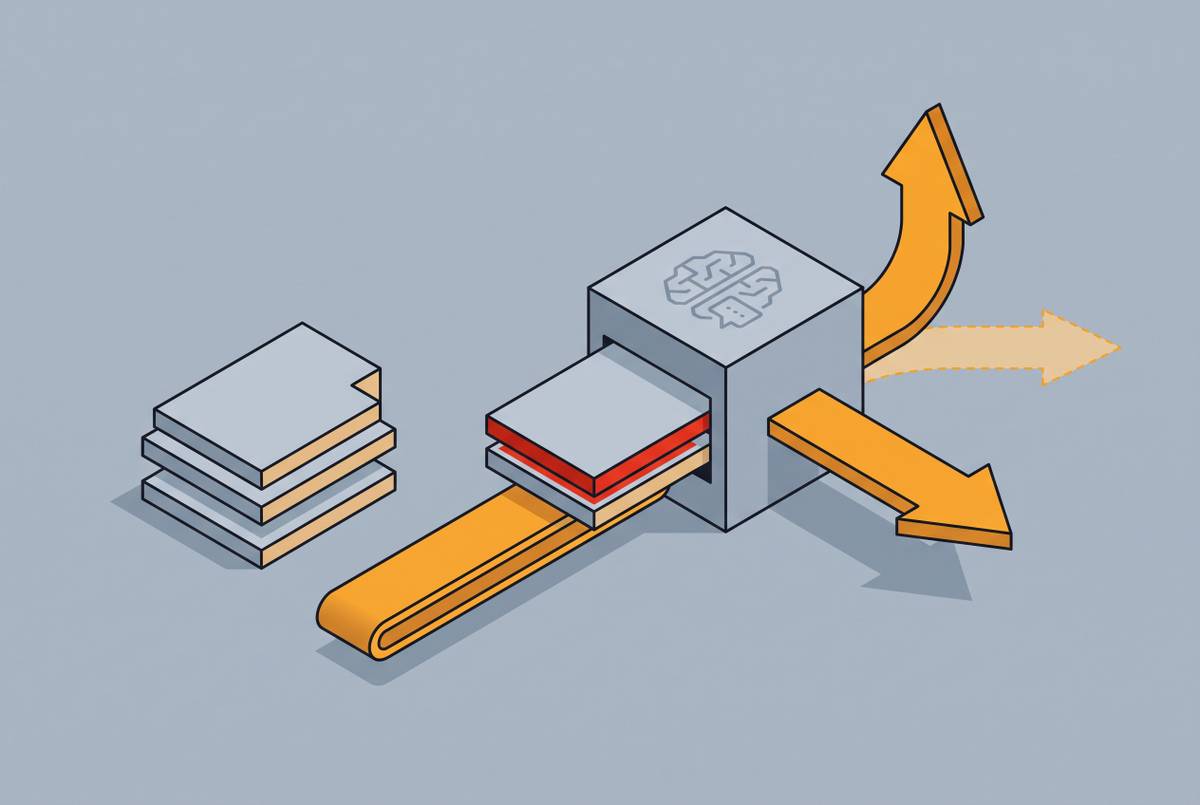
Indirect Prompt Injection via Retrieved Documents
Attackers exploit retrieved documents to inject malicious instructions into LLM systems.
Marco Quist·
 AI Security Governance
AI Security Controls in Vendor Contracts and SLAs
Contracts must rethink data rights, sub-processor chains, and performance measures for AI vendors.
Marco Quist·
 AI Vendor Risk Analysis
Vendor AI Incident Response and Breach Notification Obligations
Enterprises can't hand off AI breach liability, even when vendors fail.
Marco Quist·
 AI Vendor Risk Analysis
Open-Source LLM Supply Chain Risks in Enterprise Deployments
Enterprise security tools miss the four handoffs where open-source LLM compromises actually happen.
Marco Quist·
 AI Vendor Risk Analysis
AI Plugin and Connector Supply Chain Risks
Organizations approving AI models often miss the hidden risks in their plugins and connectors.
Marco Quist·
 AI Vendor Risk Analysis
vendors mapping AI security tools to the OWASP LLM Top 10 framework
A shared vocabulary turns risk checklist into tool comparison grid.
Marco Quist·
 AI Vendor Risk Analysis
Vendor AI Risk Assessment Template and Questionnaire Design
Rethink vendor questionnaires to catch AI risks standard security checklists miss.
Marco Quist·
 AI Vendor Risk Analysis
Evaluating Third-Party Risk Management Software for AI Coverage
Standard vendor risk software misses AI-specific threats like prompt injection and model drift.
Marco Quist·
 AI Vendor Risk Analysis
Shadow AI Risk from Unsanctioned LLM Tool Use
Data pasted into unapproved AI tools trains models that can't be unlearned or audited.
Marco Quist·
 Data Exfiltration
LLM Data Loss Prevention Tool Evaluation
Sensitive data now flows into AI tools constantly—and legacy security tools can't stop it.
Marco Quist·
 LLM Security Fundamentals
AI risk scoring and vendor assessment platforms mapped to OWASP LLM Top 10 and NIST AI RMF
Platforms claiming framework alignment vary widely in what that actually means.
Marco Quist·
 LLM Security Fundamentals
Model Denial of Service in LLM Deployments
Hidden costs in reasoning models make traditional defenses obsolete.
Marco Quist·
 Data Exfiltration in LLM Applications
How LLM Applications Leak Data Through Prompt Responses
System prompts leak easily because models can't distinguish help requests from extraction attempts.
Marco Quist·
 LLM Security Fundamentals and OWASP LLM Top 10
LLM Threat Modeling for Enterprise Applications
Here's a revised dek at 55 characters: Why LLMs shatter traditional threat modeling frameworks.
Marco Quist·