 Prompt Injection
Semantic Integrity Checks That Catch Injected Instructions Inside RAG Retrieved Chunks
Multiple detection layers catch both explicit and semantic injection attacks in RAG systems.
Selah Beck·
 LLM Security Fundamentals
How Security Teams Structure Formal AI Vendor Due Diligence Around OWASP LLM Top 10 and NIST AI RMF
Security teams now pair OWASP threat lists with NIST governance to audit AI vendors continuously.
Selah Beck·
 Prompt Injection
Evaluating Vendor Detection Capabilities for RAG-Borne and Plugin-Introduced Prompt Injection in Production
Selah Beck·
 LLM Security Fundamentals
Mapping AI Supplier Risk Assessments Across OWASP LLM Top 10 and NIST AI RMF Without Running Two Separate Programs
OWASP and NIST findings feed one supplier risk program when mapped as evidence.
Selah Beck·
 AI Agent Security
Code Execution Risks in LLM Tool Use
Securing AI agents requires isolation between instructions and data before models gain tool access.
Selah Beck·
 AI Security Governance
ISO 42001 AI Management System Requirements
The standard certifies governance systems, not model performance or fairness.
Selah Beck·
 AI Security Governance
Model Cards and AI Transparency Documentation Requirements
Regulators now require detailed AI documentation that most companies still aren't providing.
Selah Beck·
 AI Security Governance
AI-Specific Gaps in Traditional TPRM Programs
AI systems violate the three core assumptions traditional vendor risk assessment depends on.
Selah Beck·
 AI Security Governance
AI Governance Accountability Structures in Enterprises
Companies need named owners for each AI system, not just policies on paper.
Selah Beck·
 AI Agent Security
Human-in-the-Loop Controls for High-Risk Agent Actions
Approval checkpoints alone won't stop rogue AI agents from causing real-world harm.
Selah Beck·
 AI Agent Security
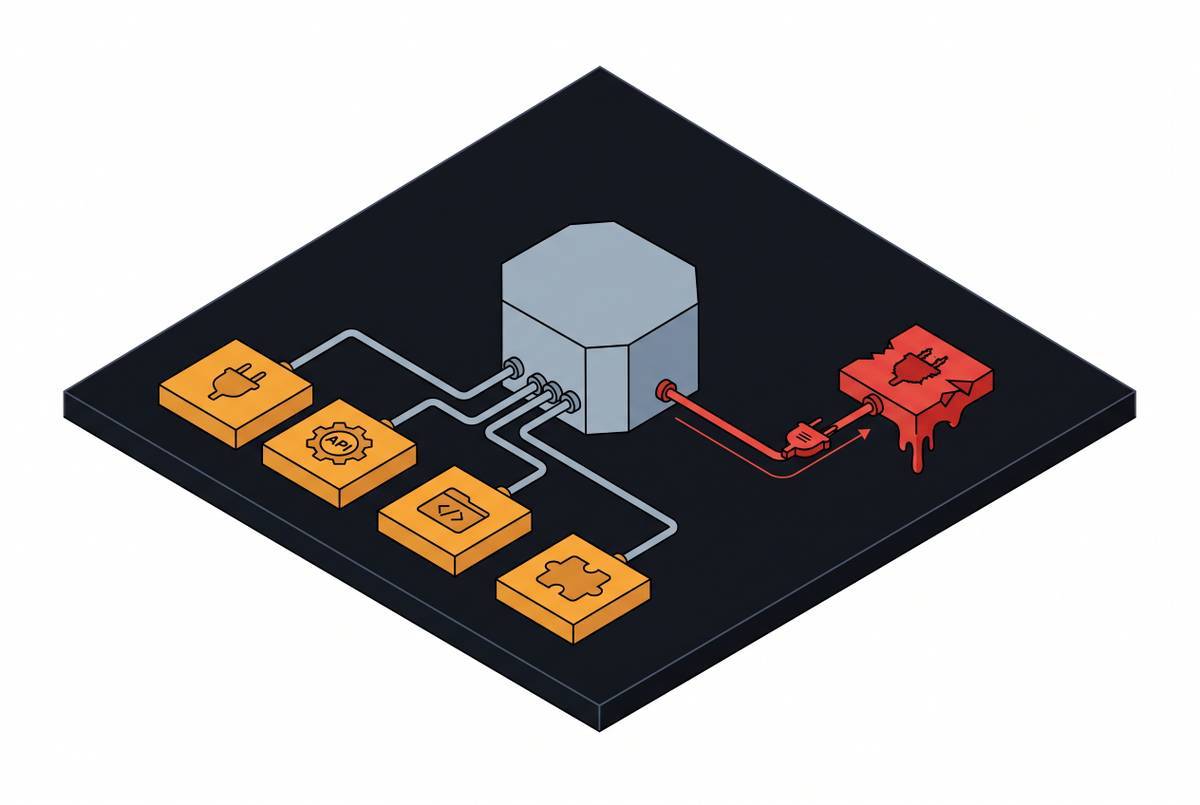
Tool Poisoning Attacks Against LLM Agents
Attackers exploit how AI agents trust tool descriptions without checking if they change mid-session.
Selah Beck·
 Data Exfiltration
Enterprise AI Security Platforms for LLM Prompt Injection and Data Exfiltration Protection
LLMs need their own security category because traditional tools can't stop prompt injection attacks.
Selah Beck·
 Prompt Injection
Mitigating Prompt Injection in Enterprise LLM Deployments
Enterprises can't patch prompt injection, but three-layer defense reduces the damage.
Selah Beck·
 LLM Security Fundamentals
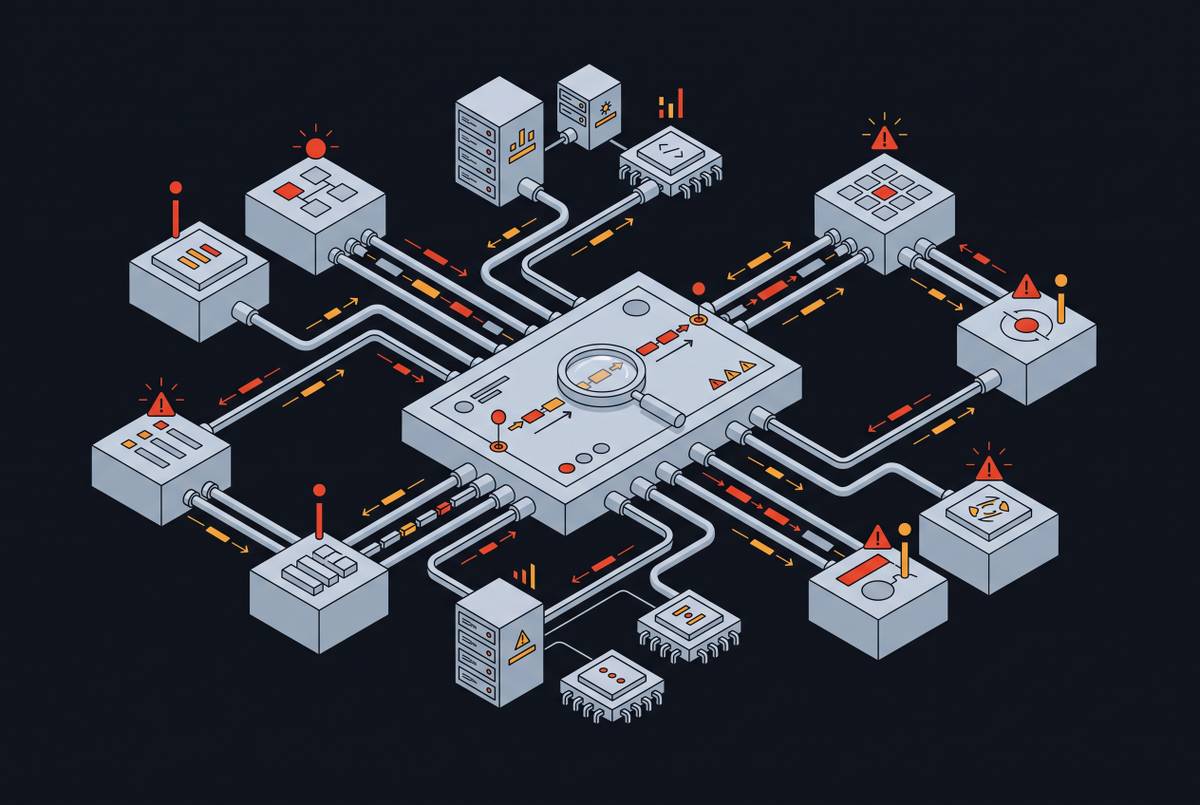
Continuous Monitoring Platforms for Third-Party AI Vendor Risk
Annual vendor reviews cannot keep pace with AI systems that change weekly or daily.
Selah Beck·
 Prompt Injection
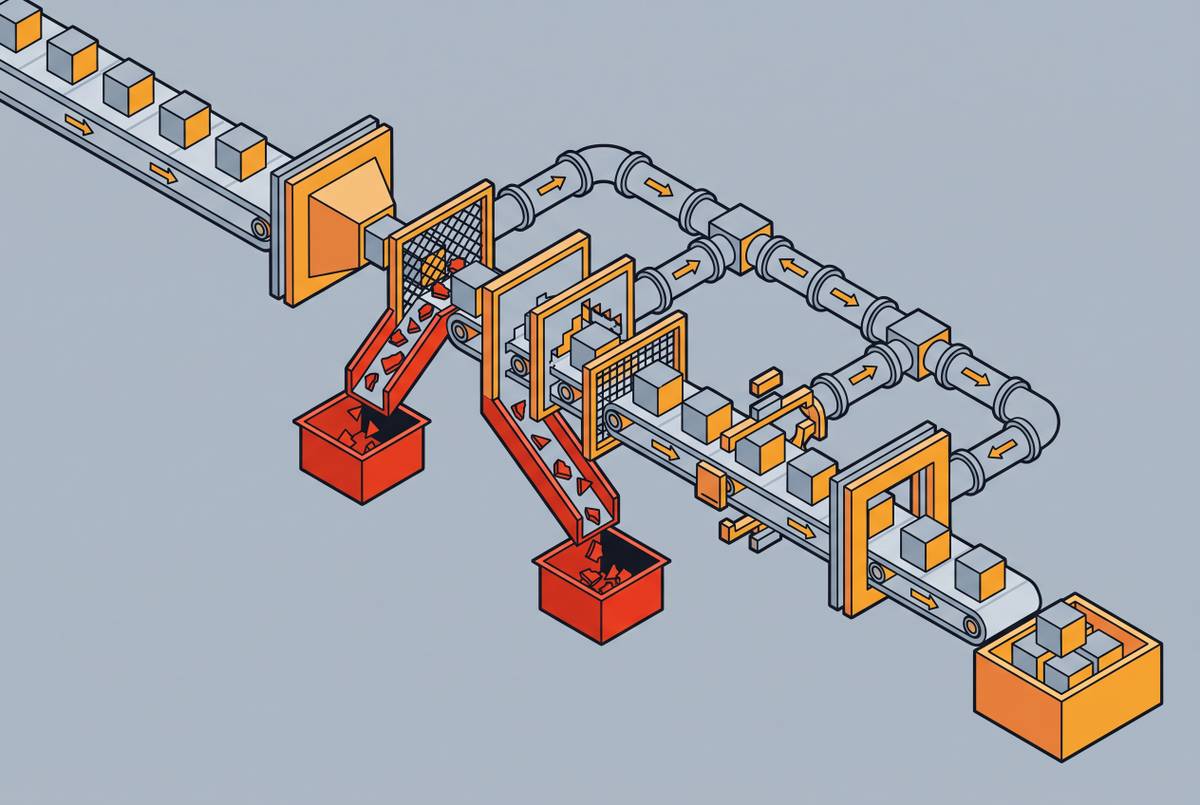
Input Sanitization Pipelines for LLM Security
Layered defenses reduce prompt injection risk, but no single pipeline can eliminate it entirely.
Selah Beck·
 Prompt Injection
Prompt Inversion and Prompt Extraction Risks
Two overlooked attacks can steal a model's secret instructions through different methods.
Selah Beck·
 Prompt Injection
 Detection Methods
Stacking four detection layers beats relying on any single method to stop prompt injection attacks.
Selah Beck·
 AI Vendor Risk Analysis
AI Security Due Diligence in Vendor Contracts
Contracts must account for AI's shifting outputs, data loops, and shared liability chains.
Selah Beck·
 AI Vendor Risk Analysis
Third-Party Risk Management for Vendor AI Features
Enterprises need new rules to spot AI features hidden inside trusted vendor software.
Selah Beck·
 Data Exfiltration
LLM System Prompt Confidentiality and Data Leakage
System prompts leak secrets because models can't distinguish instructions from user input.
Selah Beck·
 Data Exfiltration
PII Exposure in LLM Application Logs
Logging AI prompts captures personal data companies didn't mean to store.
Selah Beck·
 LLM Security Fundamentals
documented real-world prompt injection attacks against RAG-based enterprise tools
RAG systems treat retrieved data as instructions, turning documents into attack vectors.
Selah Beck·
 Data Exfiltration
System Prompt Confidentiality and Leakage
System prompts leak easily, and what's inside matters more than secrecy itself.
Selah Beck·
 LLM Security Fundamentals
Sensitive Information Disclosure via LLM Responses
Fine-tuning on sensitive data multiplies privacy leakage rates up to seventy-five percent.
Selah Beck·
 LLM Security Fundamentals and OWASP LLM Top 10
Insecure Output Handling in LLM Applications
Treating model output as trusted data opens exploitable pathways to browsers, databases, and shells.
Selah Beck·
 AI Vendor Risk and Third-Party AI Exposure
Third-Party AI Model Risk Assessment
Hallucinations and model drift pose bigger risks than security breaches most organizations ignore.
Selah Beck·